Public cloud is consumed on a meter — infrastructure, platform, database, edge. What separates a good outcome from an expensive one is how the estate is negotiated, sized, optimized and governed. Capability here is yours: the competence to consume, govern, protect and pay for it.
Most cloud problems are not technical failures. They are operating habits carried across from somewhere else.
Capabilities assembled by hand that arrived standard in the service — and now have to be maintained.
No approved catalog, no landing zone, no guardrails as code — so every decision goes through a person, or around one.
Identity handled per project, rights granted and never reviewed, protection assumed because the provider is large.
The biggest machine, always on, in an environment that bills by the hour — run by engineers who were moved to cloud rather than converted to it.
Capital became operating expense and the disciplines that governed capital did not transfer. Commitments never modeled, renewals unprepared, one provider facing no competitive tension.
No stage gates, no rollback, no cleanup, because spinning up another one was so easy.
The point of governance is for teams to move quickly without asking permission each time. Seven pillars, set once in the landing zone and the delivery pipeline, so the boundary holds without a person standing guard.
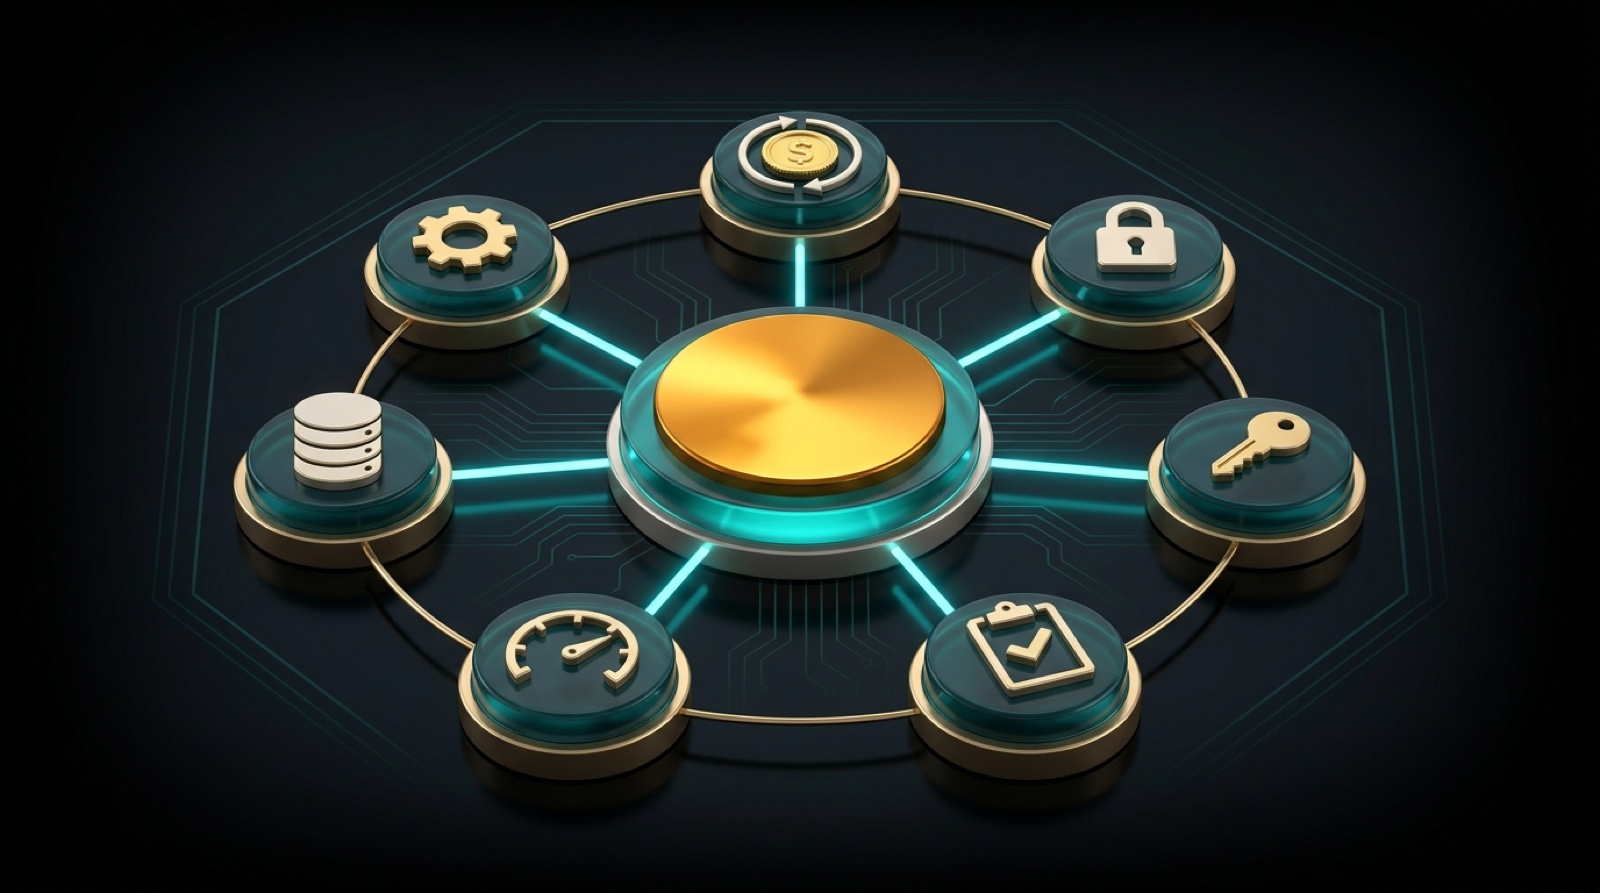
Resource deployment, budgeting, waste eliminated, pricing tiers and commitments optimized. Cost inside governance, not bolted on.
Firewall, web application firewall and DDoS protection in cloud form. The same controls, done differently.
Federation, roles, rights granted deliberately and reviewed. Who has access, and who granted it.
Regulatory mandates met by design, with data, security and compliance as one real-time view.
Reliability, visibility and performance measured. Scale down as a designed behavior.
Classified, stored and managed through its lifecycle.
Approved services, architecture, databases, operating systems and containers — standards enforced as code.
A data center is capital-intensive: you buy hardware, it depreciates, and the decision is made once. Cloud is an operating expense that scales with every resource selection — which is why sizing, scheduling, commitments and spend strategy cannot be an afterthought. They are the spend model, and AI spend now sits inside the same model.
The most expensive habit in the estate is the on-premise rule: buy the biggest server with the most memory, and leave it on. Start with the smallest machine and scale up. Shut environments down at night and on weekends. Size up for the season, not the year.
Multi-cloud is not a bad thing. Varied strengths and competitive tension are how you keep providers honest — with forecasting, show-back, charge-back, and accountability pushed back to the engineer who selected the resource.
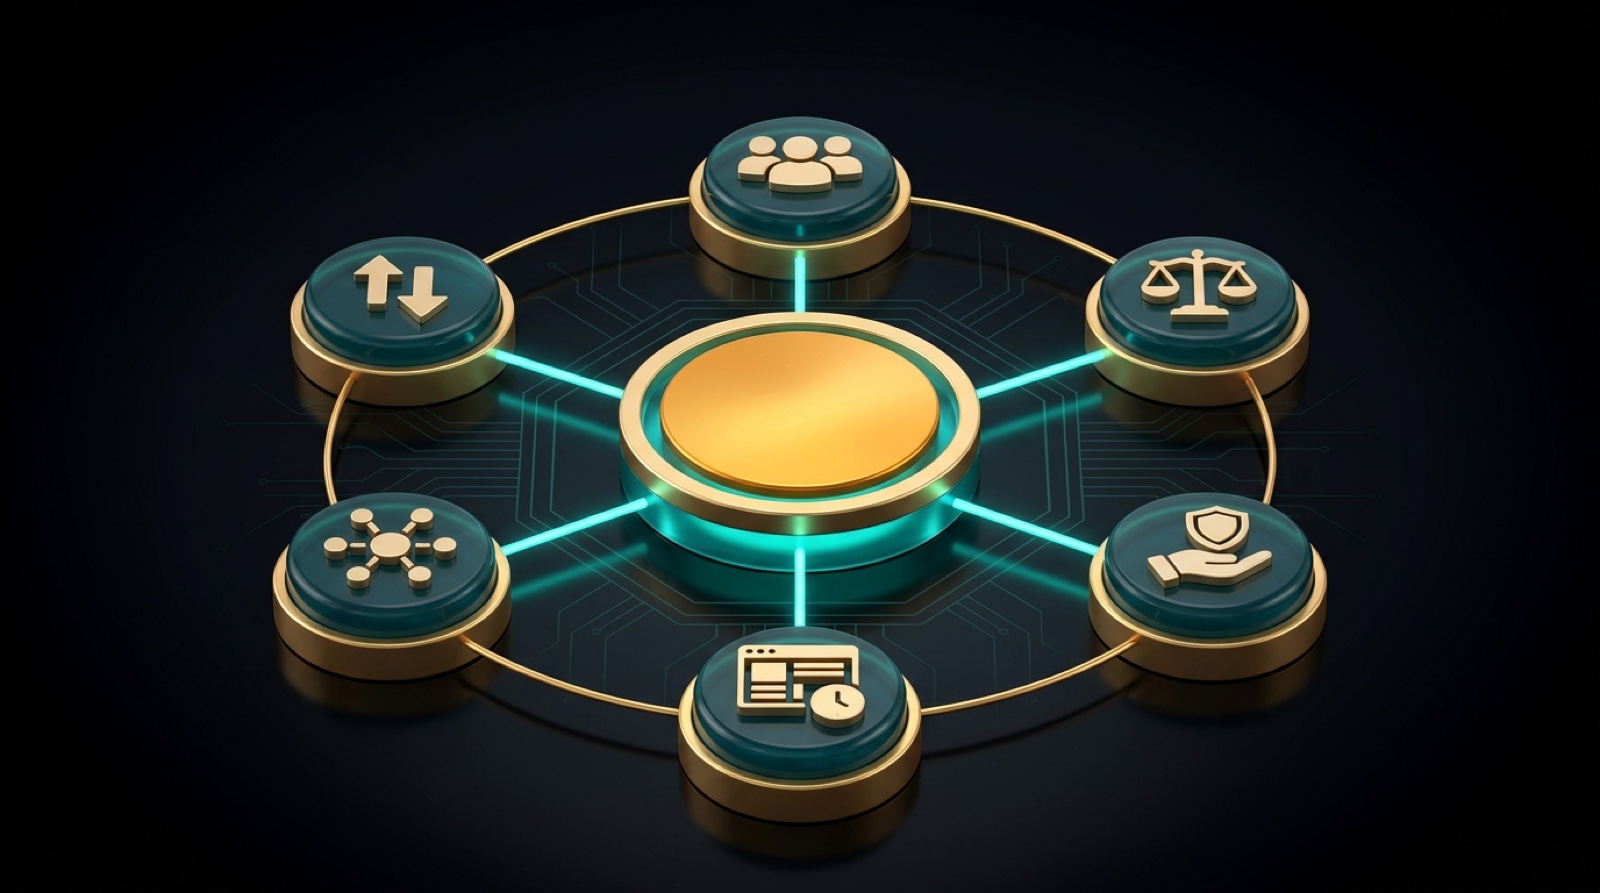
Based on the FinOps Framework — The FinOps Foundation
Landing zone first — account structure, identity, network, logging and backup policy defined once, not negotiated per project. Then governance as guardrails. Then the meter, the contracts, the team and the release discipline.
What is consumed as a service, in which form factors, from which providers — and what the platform already does before anything is built.
Account structure, identity federation, network segmentation, logging and backup policy. Approved service catalog, configuration as code.
Right-sizing, scheduling, commitments, forecasting, show-back and charge-back. Continuous optimization inside the governance frame.
What is committed, for how long, at what tension between providers. Renewals prepared. Egress and licensing found.
Stage gates soft at first and hard over time, auto-rollback, blue-green releases, security gates, observability, experiment cleanup.
On-premise engineers converted to cloud thinking, not just moved. A capability assessment and a skills path.
Ten to twenty percent year-over-year incremental savings on cloud spend, from right-sizing, plan selection, negotiation and spend governance. The percentage publishes; the method behind it is the engagement.
Before the next migration or the next renewal — what the estate actually costs, and what it should. Thirty days, an honest read, a scope of work you own.
Share Your Challenge → Or start with the thirty-day read →